NEWS
Chrome 156 Ships 353 Fixes as Rival Labs Find Critical Bugs
Chrome 156 patches 353 bugs, six of them Critical, with Anthropic and OpenAI on the credit list while Google still found 266 in-house.

Google promoted Chrome 156 to the Stable channel on October 20 with 353 security fixes, including six Critical memory bugs in Windows, Mac, and Linux builds. Desktop users should see 156.0.8078.47 or 156.0.8078.48 on Windows and Mac, and 156.0.8078.47 on Linux. The Chrome team said the build will roll out over coming days and weeks, so a copy that still shows 155 is waiting on that staged push.
The credit list is the part most how-tos skip. Google itself is named on 266 of the 353. Researcher Xinyang Ge is named on 15, four of them Critical, and OpenAI Codex Security is named on four, including the Critical WebRTC bug.
Chrome 156 Lands With 353 Security Fixes
The Stable-channel note lists 353 security fixes in Chrome 156 and points at the Chromium issue tracker for the full set. A count of that note splits the batch as 6 Critical, 61 High, 197 Medium, and 89 Low. Google did not write that any of the bugs is being used in the wild, which is the phrase it uses when it already has that evidence.
Android 156.0.8078.47 shipped the same day. ChromeOS Stable moved to 16836.19.0, with browser 156.0.8078.42, so a Chromebook is not on the desktop build number even when it has the 156-era browser fixes.
CHROME 156 BUILD NUMBERS
| Platform | Build | Shipped |
|---|---|---|
| Windows and Mac | 156.0.8078.47 or 156.0.8078.48 | October 20, 2026 |
| Linux | 156.0.8078.47 | October 20, 2026 |
| Android | 156.0.8078.47 | October 20, 2026, via Play |
| ChromeOS | 16836.19.0 (browser 156.0.8078.42) | October 20, 2026 |
If an early Stable machine is still on 156.0.8078.35 or 156.0.8078.36, those October 14 preview builds are behind this security drop and need the.47/.48 refresh.
Six Critical Memory Bugs Span Skia, CSS and WebRTC
All six Critical entries are memory bugs. Five are listed as memory corruption. The sixth is a use after free in Accessibility, meaning the browser can touch memory it has already given back. A crafted web page is the path Google describes for this class of bug, and the usual result is a crash or code running inside Chrome’s sandbox.
NIST’s record for CVE-2026-113271 scores that Accessibility use after free at 8.8 and says a remote attacker can run code inside the sandbox through a crafted HTML page, with user interaction required. Chromium still rates the same bug Critical. That gap is the sandbox: the vendor rating flags the memory bug, while the public score reflects code that has not yet left the renderer.
THE SIX CRITICAL CVE ENTRIES
| CVE | Component | Bug | Reported by | Date |
|---|---|---|---|---|
| CVE-2026-113341 | Skia | Memory corruption | October 3 | |
| CVE-2026-113279 | Accessibility | Memory corruption | Xinyang Ge | October 5 |
| CVE-2026-113072 | CSS | Memory corruption | Xinyang Ge | October 6 |
| CVE-2026-113280 | Paint | Memory corruption | Xinyang Ge | October 6 |
| CVE-2026-113271 | Accessibility | Use after free | Xinyang Ge (Anthropic), assisted by Claude | October 8 |
| CVE-2026-113303 | WebRTC | Memory corruption | OpenAI Codex Security (kylebot) | October 15 |
Google found the Skia bug in its own graphics engine. Ge’s four Critical reports sit in Accessibility, CSS, and Paint, the parts of Chrome that style pages, draw them, and expose them to assistive tech. The WebRTC bug, filed a week later, is the one OpenAI Codex Security put its kylebot handle on.
Anthropic and OpenAI Show Up on the Credit List
The Stable note now reads like a lab roster. Five of Ge’s 15 bugs in this drop, including CVE-2026-113271, are tagged “Xinyang Ge (Anthropic), assisted by Claude.” The other Claude-tagged items in this build are High bugs in Date, ServiceWorker, DisplayLocking, and PDF. That wording is a human report with a named model, not a claim that Claude ran unattended.
OpenAI Codex Security is credited on four bugs in the same note. Besides kylebot’s Critical WebRTC report on October 15, the list already names OpenAI Codex Security (amyb) on a High use after free in V8 (CVE-2026-113044) and a High use after free in Turbolev (CVE-2026-113338). The handles sit in the same field Google has used for outside researchers for years.
This is not Ge’s first Chrome line in October. The October 15 Stable refresh, which fixed 10 bugs in 155.0.8059.84/.85, already credited “Xinyang Ge (Anthropic), assisted by Claude” on a High DOM memory-corruption bug. Chrome 156 is a larger showing of the same credit style, not the debut.
Access to bug details and links may be kept restricted until a majority of users are updated with a fix.
Chrome team, Stable Channel Update for Desktop
Google also said it will keep those restrictions when a bug sits in a third-party library that other projects still have not patched. The practical effect is that the six Critical names are public while the reproduction steps are not, which is the usual race after a browser patch: attackers diff the binary, users wait on a restart.
A Milestone Release Looks Like a Flood
Three desktop security notes landed in seven days. October 13 moved Chrome 155 to 155.0.8059.79/.80 with 37 fixes, seven of them Critical. October 15 added 10 more, one Critical. October 20 then promoted milestone 156 and emptied its security bucket in one Stable push. The milestone 156 security-fix tracker is that bucket, which is why 353 sits next to a prior refresh of 10 without meaning 35 times as many bugs were found in a week.
OCTOBER DESKTOP SECURITY NOTES
- October 13, 2026: Chrome 155.0.8059.79/.80 (Linux 155.0.8059.79) with 37 security fixes, seven Critical.
- October 15, 2026: Chrome 155.0.8059.84/.85 (Linux 155.0.8059.84) with 10 security fixes, one Critical, including Ge’s Claude-assisted DOM bug.
- October 20, 2026: Chrome 156.0.8078.47/.48 (Linux 156.0.8078.47) with 353 security fixes, six Critical.
Google still found most of the 156 list. Two hundred and sixty-six internal credits is the bulk of the work, much of it the High and Medium memory bugs that never make a consumer headline. The change is at the top of the severity ladder, where a rival lab’s researcher and a rival lab’s security handle now share the Critical row with Google’s own Skia report.
High bugs in the same note still hit Site Isolation, FileSystem, ANGLE, V8, GPU, Navigation, and Passwords. Those are the layers a memory bug has to cross before a web page becomes a machine-wide problem, which is why a Critical renderer bug is urgent and still not the same thing as a full Chrome exploit.
VinFast Engineer Collects $10,000 for Site Isolation
Outside researchers who are not on a lab payroll still get paid, and the largest listed check in this note is not one of the Critical six. CVE-2026-113101, a High use after free in Site Isolation, paid $10,000 to Quyen Son at VinFast (@zer0qs), who filed it on September 13. Site Isolation is the feature that tries to keep one site’s renderer from reading another site’s data, so a bug there is the kind of finding the bounty program is built to buy.
BOUNTY CHECKS IN THIS RELEASE
- Top listed payout: $10,000 for the Site Isolation use after free filed by Quyen Son at VinFast.
- FileSystem High: $3,000 to nh.dev2022 for a use after free filed June 21.
- Other listed Highs: several $2,000 and $1,000 awards for ANGLE, WebUI, Network, Passwords, CacheStorage, SVG, V8, and Accessibility reports.
- Internal and pending: Google-credited bugs show N/A, and several outside reports still show TBD.
A week before 156 hit Stable, Google Bug Hunters quadrupled memory-corruption base rewards to $2,000 and posted payouts of up to $20,000 for a controlled write from web contents in the browser, network, or GPU process. Renderer writes and use-after-free bugs go up to $8,000 on that table. The $10,000 Site Isolation check is this release’s largest published award; the $20,000 figure is the program ceiling for a different, higher-impact class, not a second number for the same bug.
Downloading Chrome 156 Does Not Finish the Job
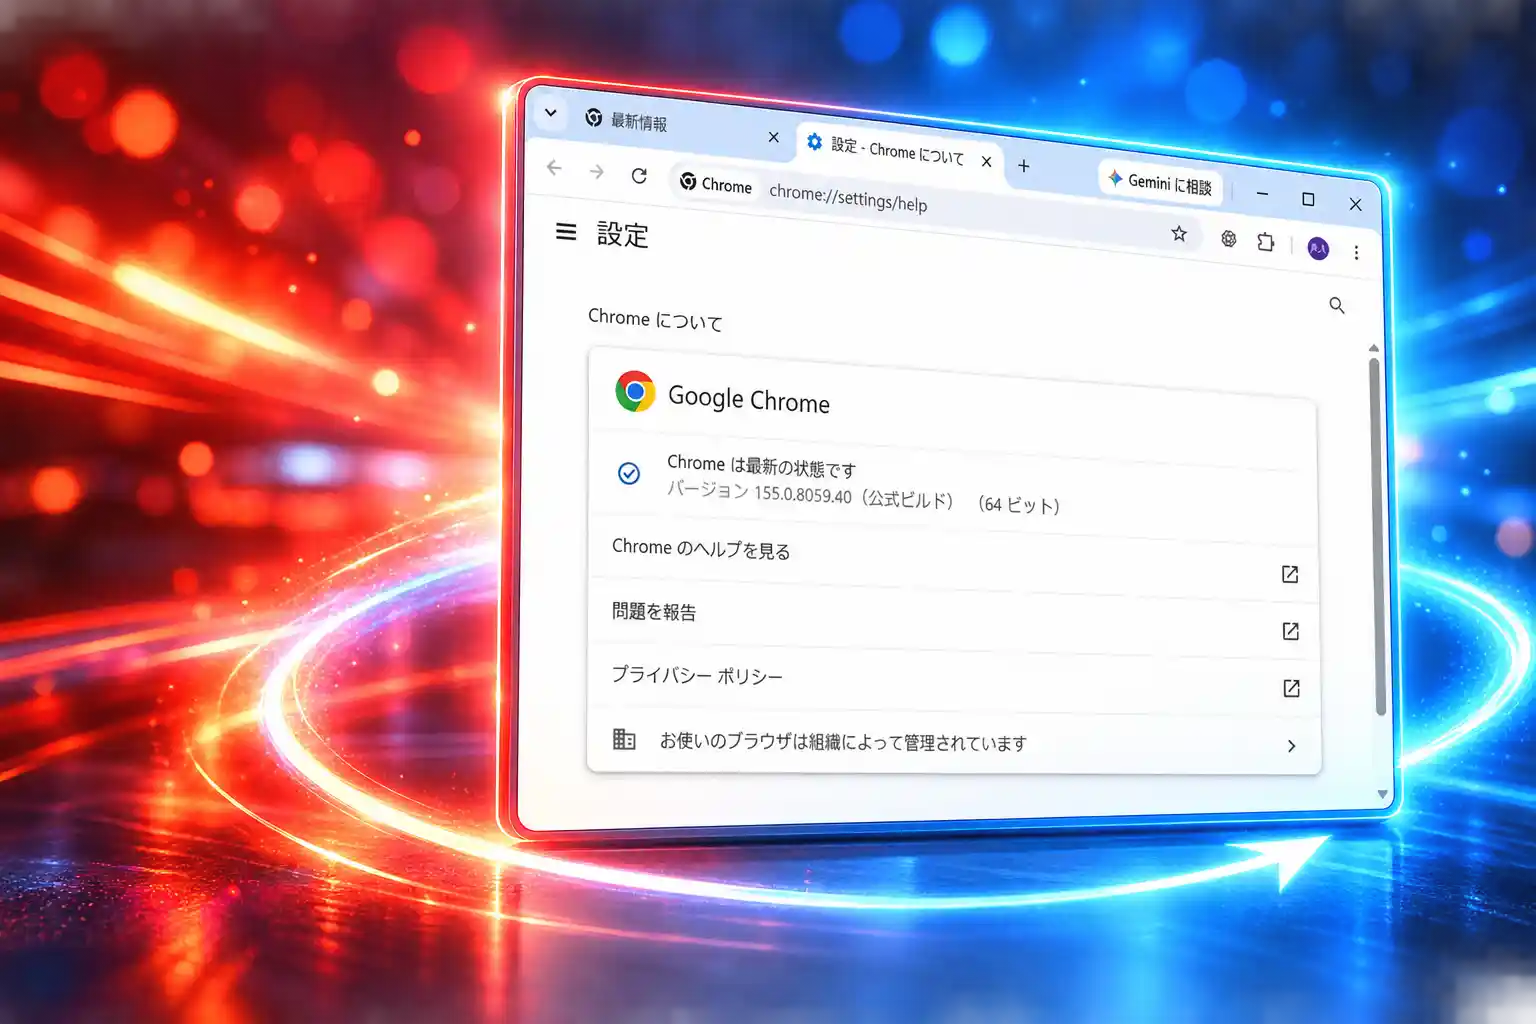
Chrome can finish the download and still run the old code until the process exits. That is the step people with a pile of tabs keep putting off, and it is the step that actually loads 156.0.8078.47 or 156.0.8078.48. On October 22, some desktops were still reporting 155.0.8059.85, which is the October 15 build, because Stable had not reached them yet or because nobody had opened the About page.
HOW TO FINISH THE CHROME 156 UPDATE
- Open About: Type chrome://settings/help in the address bar, or use the three-dot menu, then Help, then About Google Chrome.
- Read the build: Windows and Mac need 156.0.8078.47 or 156.0.8078.48; Linux needs 156.0.8078.47.
- Wait if you must: If the number is still 155.0.8059.84 or 155.0.8059.85, Chrome has not been offered 156 on that machine yet; check again later.
- Relaunch: The new code is not active until you click Relaunch. Ordinary tabs come back; an Incognito window does not, so save anything you were typing there first.
- Offices: IT admins can push the build with Chrome Enterprise tools and set a relaunch deadline, because a silent download on a machine that stays open for days does nothing.
Japan’s National Cybersecurity Office pointed operators at the October 20 desktop note and told them to apply the update once it arrives. That is the right order: confirm the build number, then restart, then confirm the number again.
Android Follows Desktop as Extended Stable Lags
Krishna Govind’s Android note says 156.0.8078.47 will show up on Google Play over the next few days and that Android builds carry the same patches as the matching desktop releases unless the note says otherwise. Phone users still have to let Play finish and then swipe Chrome out of recents so the new process starts. Extended Stable is on a slower train; shops that pin that channel were on 152.0.7977.169 after the October 15 follow-up and do not pick up 156’s 353-fix list until Google moves that channel.
WHAT WE KNOW
- Shipped builds: 156.0.8078.47/.48 on desktop, 156.0.8078.47 on Android, ChromeOS 16836.19.0 with browser 156.0.8078.42.
- Severity split: 353 fixes, six Critical, with Google silent on in-the-wild use.
- Credits: Google 266, Xinyang Ge 15 (five tagged Anthropic, assisted by Claude), OpenAI Codex Security four.
WHAT IS UNCONFIRMED
- Active exploits: Google did not say any of these six Critical bugs is being used, and it did not say they are unused either.
- Other Chromium browsers: Edge and other Chromium builds need their own releases; this note does not ship those version numbers.
- Bug write-ups: Full details stay restricted until most users are patched, and longer if a shared library is still open.
The About page is the only check that matters on a given machine. If it does not yet read 156.0.8078.47 or 156.0.8078.48, the six Critical fixes are still sitting in someone else’s build.

Bulk Scotch Still Faces Full Duty After India’s UK Deal

Typhoon Champi Loops Off Taiwan and Still Injures 527

PM Modi Opens Chinmaya’s AI Guru and Asks for Unity

Mahim Police Hold a JeM Suspect on Enmity Charges

Gold Falls Below $4,000 as Hormuz Oil Hits $117

The iPhone 18 Pro Max Splits Apple’s Fall in Two

OpenAI Calls GPT-6 Astra AGI Then Locks Its Exploits

Clancy Juror Says the Holdout Never Cited Evidence

Trump Claims Hormuz Control as Oil Holds Near $96

Russia Closes the Goethe-Institut Berlin Tried to Save

 NEWS2 months ago
The iPhone 18 Pro Max Splits Apple’s Fall in Two
- NEWS2 months ago
OpenAI Calls GPT-6 Astra AGI Then Locks Its Exploits
- NEWS1 month ago
Clancy Juror Says the Holdout Never Cited Evidence
- BUSINESS2 months ago
Trump Claims Hormuz Control as Oil Holds Near $96
- LIFESTYLE2 months ago
Russia Closes the Goethe-Institut Berlin Tried to Save
- AUTO2 months ago
Volkswagen’s Job Cuts Leave Four Plants Without Cars
- NEWS2 months ago
Dyson Puts Nurovi Robots on Sale Without the UV Flagship
- NEWS2 months ago
The Lincoln’s 286-Day War Cruise Ends at a Thai Pier